

A public security review has raised alarms about Huntarr security vulnerability, prompting users to take the tool offline following claims of exposed API endpoints and stored API keys without authentication.
Given Huntarr’s role as a central automation hub for *arr services like Sonarr and Radarr, the reported flaws quickly raised concerns about broader credential exposure across connected applications.
Why are users being urged to shut down Huntarr?
According to the publicly shared GitHub review, Huntarr v9.4.2 contained authentication bypass flaws that could allow unauthenticated access to internal API endpoints. The review states that stored API keys and configuration settings could be retrieved without logging in.
The findings described in this article are based on a publicly shared Reddit post and a GitHub security review. As of publication, the reported vulnerabilities have not been independently verified, and no official response from the Huntarr maintainers has been publicly released.
TL;DR: Huntarr security review highlights
A security researcher published a detailed review outlining multiple alleged flaws in Huntarr and shared the findings on Reddit, where the post gained traction within hours. Community members began advising users to shut down the application, rotate API keys for connected services, and review logs for suspicious activity. Soon after, community reports noted that the project’s subreddit and main GitHub repository became inaccessible, further escalating concern. As of publication, users are being urged to assume credentials may have been exposed and take precautionary steps.
What are the key security vulnerabilities reported in Huntarr?
According to the Reddit post and the GitHub review, multiple vulnerabilities were identified in Huntarr v9.4.2.
- Authentication bypass: The reviewer alleges that certain API endpoints could be accessed without a valid login session. According to the review, this would allow anyone on the same network, or on the internet, if the instance were exposed, to interact with the application without authentication.
- Exposure of stored API keys: The report claims that configuration endpoints returned stored API keys in cleartext. Because Huntarr integrates with services such as Sonarr, Radarr, and Prowlarr, retrieving those keys could enable unauthorized access to connected applications. The review characterizes this as cross-application credential exposure, meaning multiple connected services could potentially be affected at once.
- Account takeover concerns: The disclosure references authentication-related endpoints, including two-factor authentication (2FA) setup routes, that the review describes as accessible without proper verification. The reviewer states this could allow an attacker to retrieve authentication secrets and register their own device.
- Unauthorized configuration and recovery actions: Additional endpoints were reportedly capable of modifying setup state, generating recovery keys, or re-arming account creation without login. The review indicates these behaviors could allow unauthorized reconfiguration of the application.
In the GitHub review outlining the alleged flaws, the author writes:
“If you run Huntarr and it’s reachable on your network, anyone can read your passwords and rewrite your config right now. No login required.”
Huntarr Security Reproduction Lab (GitHub)
Who is most at risk in the Huntarr API key exposure?
Users whose Huntarr instances were accessible on a local network or exposed to the internet face the highest potential risk, since those deployments could have been reached without authentication. Public-facing setups carry the greatest exposure, and users who have not rotated API keys since the disclosure may remain vulnerable if credentials were accessed.
In the GitHub review, the author categorized several findings as “Critical” and “High” severity, including unauthenticated settings access, cross-app credential exposure, and 2FA-related issues.
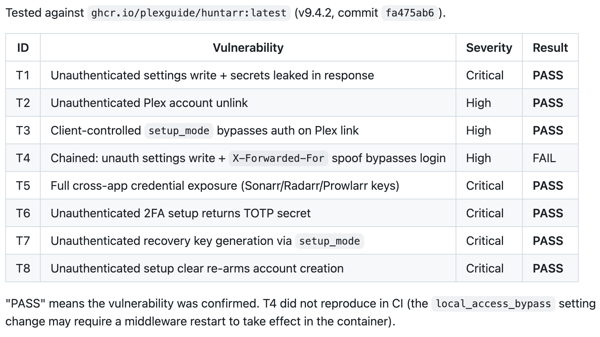 Source: rfsbraz/huntarr-security-review (GitHub)
What happened after the disclosure of Huntarr’s critical vulnerabilities?
The security concerns gained visibility after posts detailing the alleged flaws were shared on Reddit and GitHub. The discussion quickly gained traction, with users urging others to shut down Huntarr and rotate API keys as a precaution.
Several community forums began circulating warnings, and tech-focused sites and social posts amplified the discussion, further increasing visibility around the reported issues.
Soon after the thread gained attention, community members reported that the project’s subreddit had been made private and that the main GitHub repository was no longer publicly accessible.
As of publication, no official statement, confirmed patch, or formal security advisory addressing the reported findings has been publicly released by the Huntarr maintainers.
Source: GitHub/Huntarr.io
What should Huntarr users do now?
Community discussions after the disclosure have prompted users to adopt precautionary measures.
- Shut down the Huntarr instance if it is still running, particularly if it was accessible on a local network or exposed to the internet.
- Regenerate all API keys for connected services, including Sonarr, Radarr, Prowlarr, and any other integrated applications.
- Reset related credentials and review account security settings, including authentication methods.
- Check system logs and configurations for unexpected changes, new devices, or unfamiliar activity.
Why does this matter for software buyers and security teams?
While Huntarr is commonly associated with self-hosted setups, the broader issue extends to any tool that stores API keys and connects multiple services. Applications that function as integration hubs effectively become centralized access points and, in some cases, centralized risk points.
For software buyers comparing automation and integration tools on platforms like G2, incidents like this highlight the importance of evaluating how products manage authentication controls and credential storage. A single weak point in an integration-heavy tool can potentially expose connected systems across an environment.
For security and IT teams, structured vulnerability management practices, supported by dedicated vulnerability management tools, help surface misconfigurations and access gaps before they escalate. Regular security assessments, including vulnerability testing and penetration testing, play a critical role in identifying weaknesses across connected systems.
The bigger takeaway
The Huntarr security vulnerability discussion shows how quickly concern escalates when an integration-heavy tool is accused of exposing credentials. Within hours of the review surfacing, users were urging shutdowns and rotating API keys, a reminder of how central these tools become in connected environments.
Whether or not the reported findings are formally addressed, the episode underscores a broader reality for modern software stacks: applications that store API keys and bridge multiple services carry amplified risk. When authentication controls are questioned, the impact can ripple across an entire ecosystem.
For organizations exploring proactive security testing, G2’s guide to the best penetration testing tools offers a comparison of top solutions designed to surface vulnerabilities early.
