

by BLACK ENTERPRISE Editors
November 24, 2025
Patients, employees, and others can also file complaints within 180 days of the breach. Complaints need to include who was involved and what happened.
HIPAA violations don’t always come from malicious attacks or headline-making data breaches. More often, they stem from everyday mistakes, like misdirected emails and vendors that aren’t as secure as they seem. Even small slip-ups can expose protected health information (PHI) and invite major consequences.
In today’s complex compliance landscape, those mistakes are alarmingly common. In fact, 60% of respondents in our latest survey said their organization has experienced a HIPAA-related incident or near miss.
Vanta surveyed over 600 healthcare professionals to find out where organizations are most at risk. The results show that HIPAA-related incidents are surprisingly common and reveal clear gaps in vendor oversight, staff training, and risk management.
Key takeaways
- 60% of respondents said their organization has experienced a HIPAA-related incident or near miss, showing how common HIPAA-related incidents are.
- 41% of organizations cite evolving regulations as their top challenge for staying HIPAA-compliant.
- 59% of organizations are very confident that their vendors are HIPAA compliant, but only 33% conduct annual vendor risk assessments.
- Only 69% of organizations demand HIPAA training from vendors, revealing vulnerabilities.
What is a HIPAA violation?
A HIPAA violation occurs when PHI is handled in a manner that violates the standards set by the HIPAA Privacy, Security, or Breach Notification Rules. Whether it’s an employee mistake or vendor breach, the result is the same: exposed data and organizational risk.
HIPAA compliance requirements apply to both covered entities and business associates. Covered entities include health plans, healthcare providers, and clearinghouses that create or manage PHI. Business associates are vendors or partners that handle PHI on behalf of these organizations, such as billing services or cloud storage providers. Both are legally obligated to safeguard PHI and can face penalties if they fall short.
While maintaining HIPAA compliance is a must for legal reasons, it’s also crucial for earning and maintaining patient trust. Violations can lead to hefty fines and lost clients, both of which can take a serious toll on your business.
HIPAA compliance remains a struggle, especially around vendors and evolving rules
Despite increased awareness, many organizations still face significant hurdles in meeting HIPAA compliance requirements. This is especially true when working with third-party vendors and keeping up with changing regulations. Our latest survey reveals where teams are falling short and what’s causing the most concern in 2025.
60% of organizations reported a HIPAA-related incident or near miss
HIPAA violations are more common than many organizations would like to admit. Even with safeguards in place, compliance often breaks down in day-to-day operations.
These lapses aren’t always headline-grabbing breaches; they’re often the result of small, preventable errors, such as sending an email to the wrong person or forgetting to secure physical records. Still, the consequences can be serious, from exposed personal health information to that data ending up on the dark web.
In our recent survey, 60% of respondents said their organization has experienced a HIPAA-related incident or near miss. Nearly a third reported a confirmed violation, and another third cited internal alerts or close calls.
This frequency speaks to how difficult HIPAA compliance is to maintain in the real world, especially when human error and operational complexity are involved.
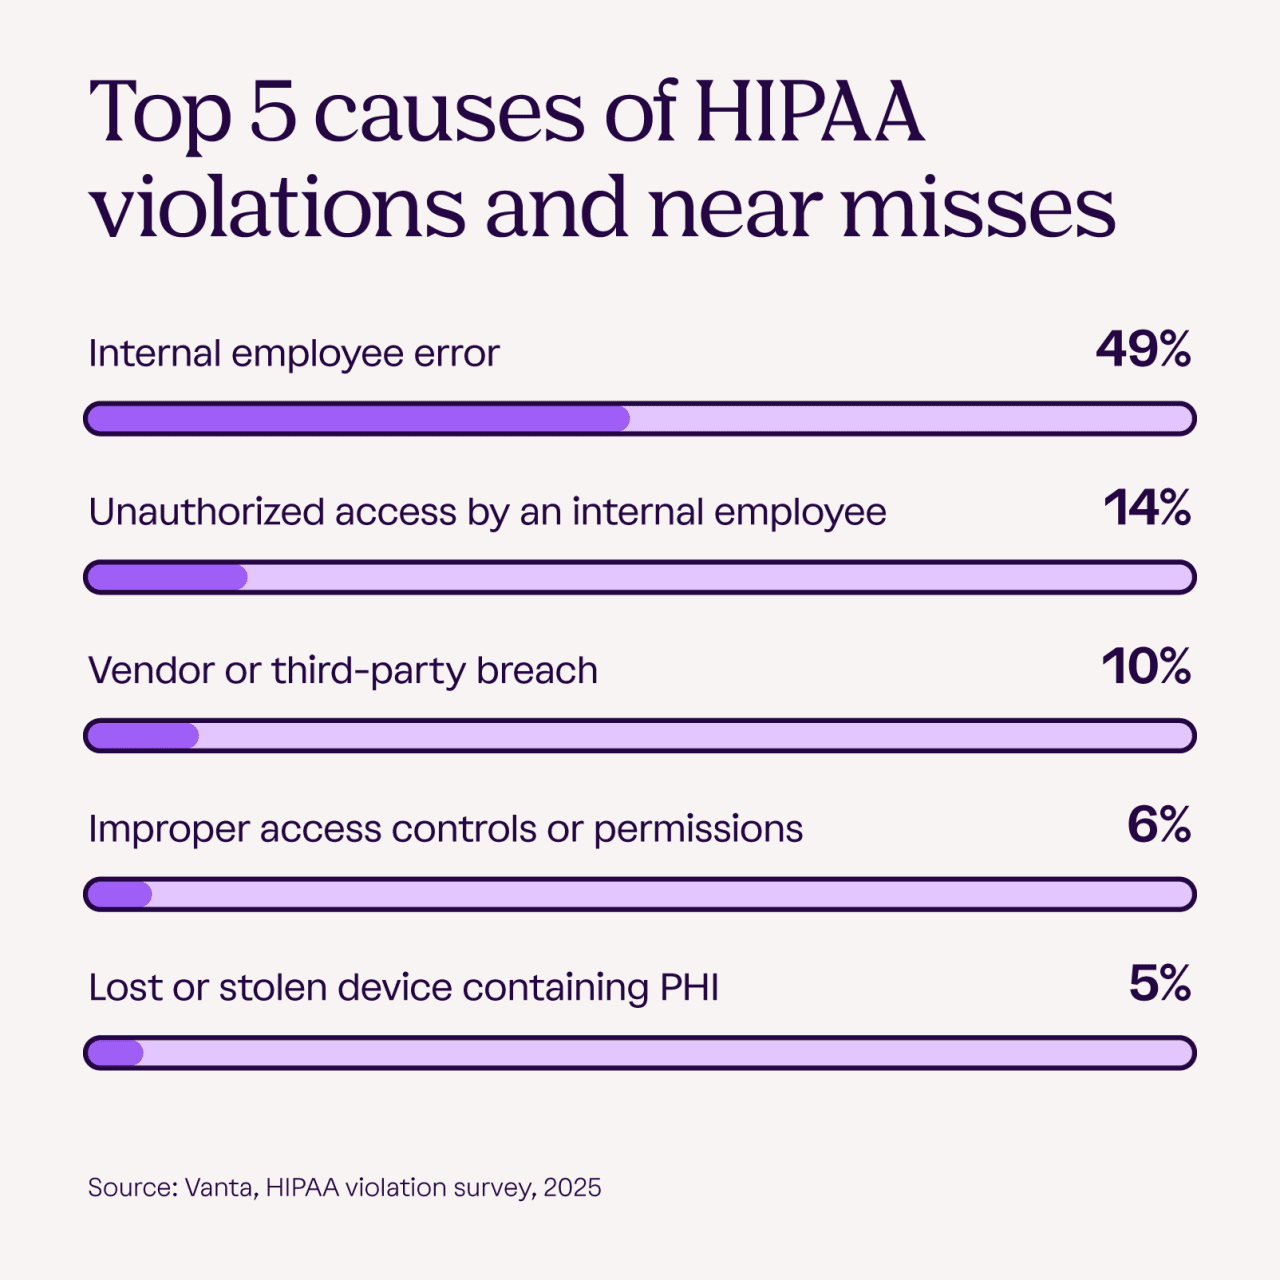
Most of these violations and near misses come from within the organization, not from external attacks. Internal employee error was the most commonly cited cause of HIPAA-related incidents, including misdirected emails, improper record disposal, and failure to follow standard procedures.
Here’s how the top causes break down:
- 49%: Internal employee error
- 14%: Unauthorized access by an internal employee
- 10%: Vendor or third-party breaches
These trends reinforce the importance of strong internal controls, especially access management, employee training, and clear data handling. They also highlight the need for better oversight of third-party vendors, since your compliance risk extends to everyone who touches your PHI.
For organizations looking to tighten their defenses, a HIPAA compliance checklist is a useful starting point for building smarter, more proactive strategies.
Regulations, staff training, and third-party tools are the biggest headaches in HIPAA compliance
HIPAA compliance isn’t a one-time action. As regulations shift and technologies evolve, new threats to staying compliant emerge. Organizations are responsible for keeping up with these changes and ensuring they use HIPAA-compliant software and tools that can adapt to evolving risks.
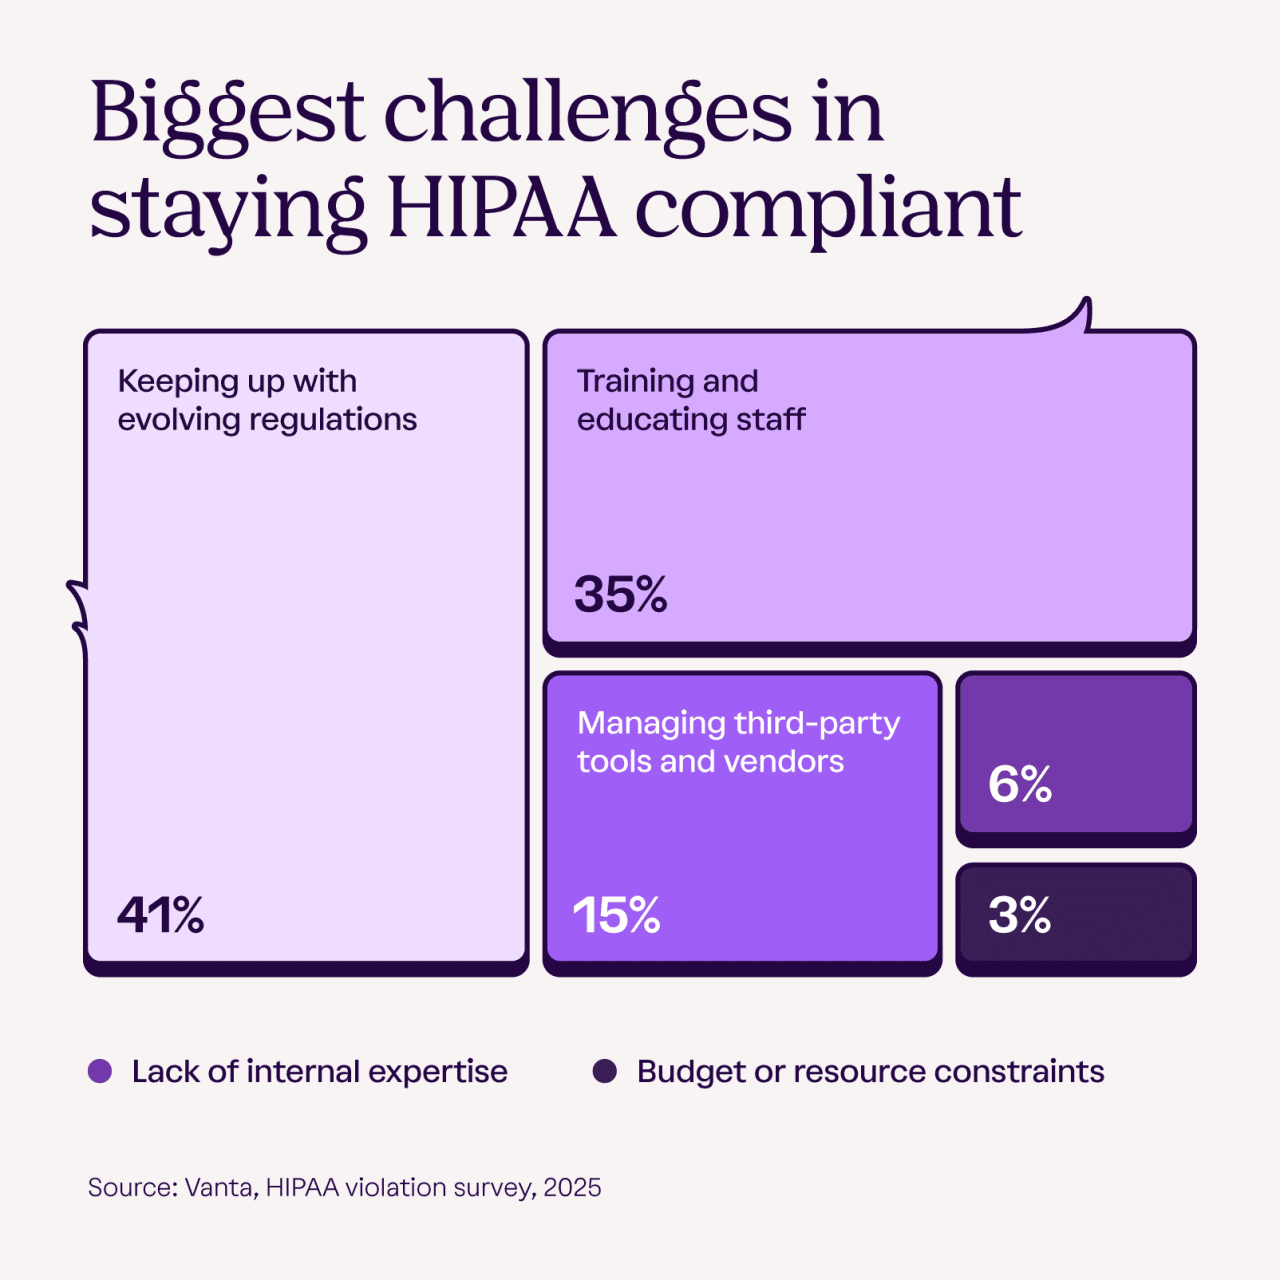
When asked about their biggest compliance challenges, 41% of organizations cited evolving regulations as their top concern. Training and educating staff came next, cited by 35% of respondents, followed by managing third-party tools and vendors at 15%.
These numbers highlight just how layered HIPAA compliance has become. It’s an ongoing effort that demands clear policies, consistent training, and tight oversight across the entire organization while also balancing day-to-day operations.
Without a clear, coordinated plan, even the most well-intentioned teams can fall behind, leaving the door open to costly HIPAA violation fines.
“The upcoming updates to HIPAA represent a meaningful modernization, particularly regarding the Security Rule, to better align with today’s evolving cybersecurity landscape. Removing ‘addressable’ safeguards means organizations will need to transition controls such as multi-factor authentication (MFA), encryption, and screen locks, from discretionary measures to mandatory requirements, pushing a stricter security posture. Additionally, the new emphasis on ‘availability’, including backup strategies and disaster recovery plans, introduces requirements that are standard IT practices, but new for HIPAA enforcement. While changes to the Privacy Rule may not be as extensive, we can expect greater emphasis on proper access, disclosure, and patient data handling.” – Faisal Khan, GRC Solutions Expert, Vanta.
To stay ahead of potential violations, most organizations are investing in a layered defense. According to our survey, 83% of organizations provide HIPAA-specific compliance training for employees, 65% use data encryption and access controls, and 64% have internal audit or compliance monitoring systems.
This growing mix of strategies shows that HIPAA compliance isn’t solved by a single tool or policy. It requires a coordinated effort across training, technology, and oversight.
While many organizations are investing in employee education, the high rate of internal errors suggests that training needs to be more effective and ongoing to ensure proper risk mitigation.
59% of organizations feel vendors are HIPAA compliant, but regular risk assessments are rare
Staying HIPAA-compliant means protecting your systems and ensuring your vendors meet the same standards.
Although many organizations express confidence in their vendors’ compliance, few actively verify it regularly, creating blind spots that can lead to costly violations.
In our survey, 59% of respondents said they are very confident their vendors are HIPAA-compliant, but that trust isn’t always backed by action.
In fact, only 41% of respondents conduct a risk assessment of vendors during onboarding, and only 33% conduct annual vendor assessments. Without consistent processes in place, vendors that were once compliant may fall out of step over time. This can lead to weak points in an otherwise secure system.
These findings underscore the need for structured, ongoing evaluations, not just at the start of a relationship. HIPAA compliance verification and regular third-party risk assessments are essential to maintaining a strong, end-to-end compliance posture.
Only two-thirds of organizations demand HIPAA training from vendors
While many organizations have a handle on their internal policies, vendor compliance can be hard to monitor. It’s not always clear how well third-party partners are managing sensitive data.
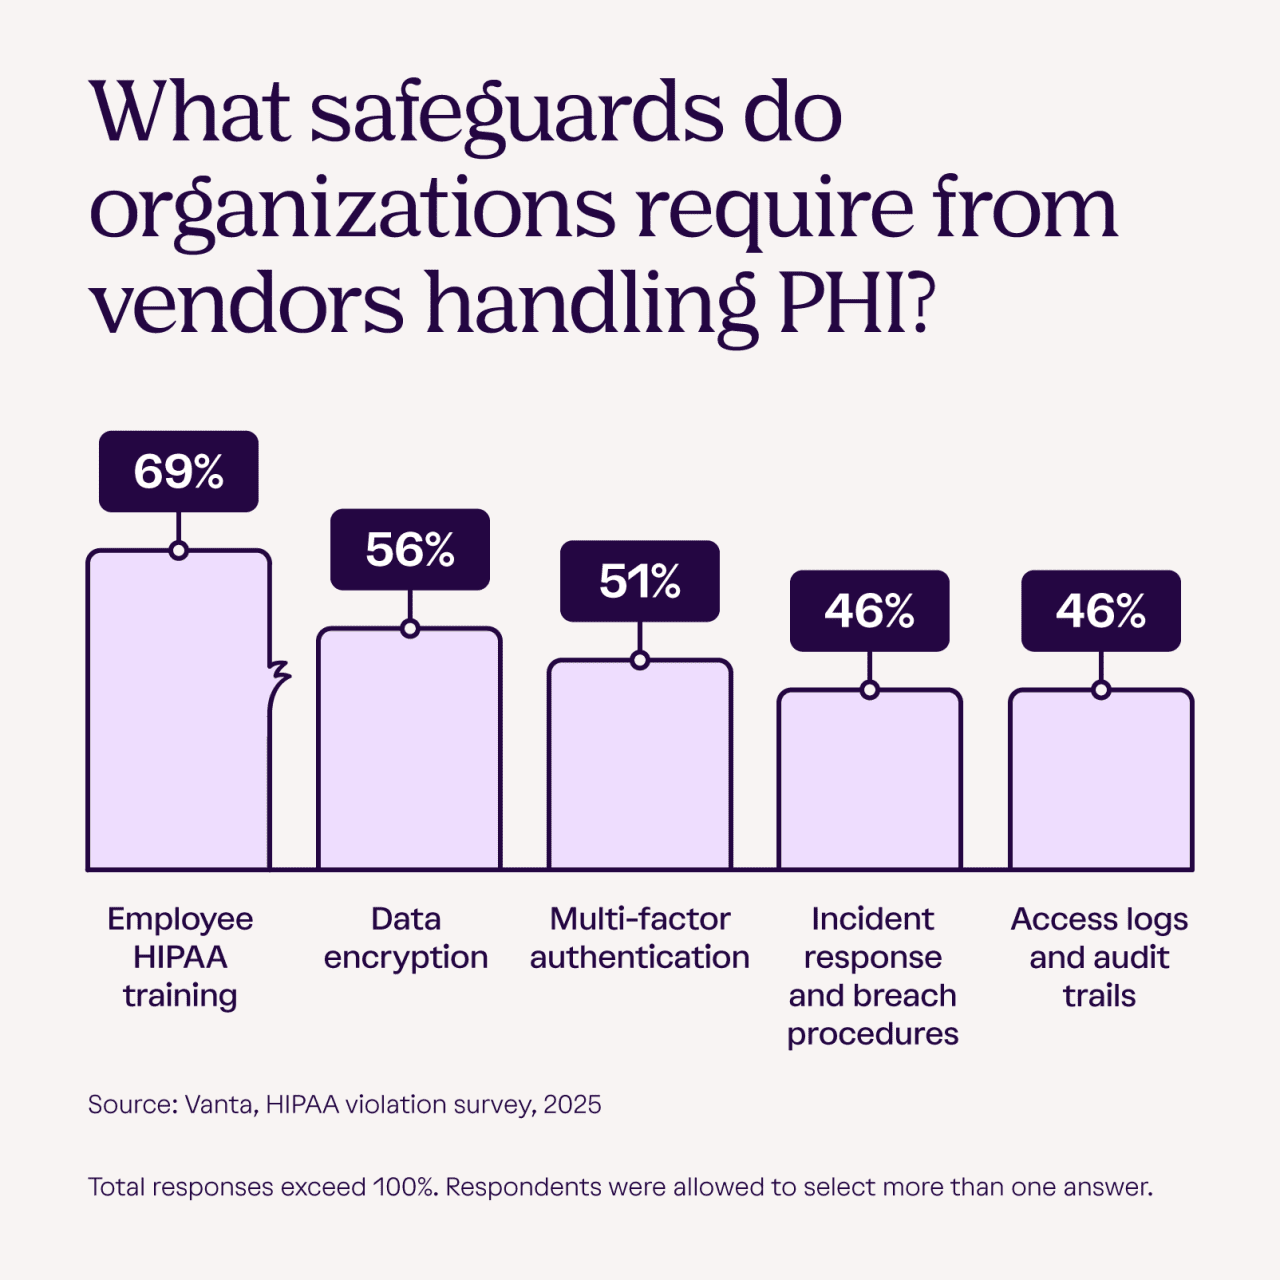
According to our survey findings, just 69% of organizations require vendors to provide employee HIPAA training and show compliance verification.
Adoption of other safeguards is even lower: Data encryption is required by 56% of organizations, multi-factor authentication by 51%, and incident response procedures by 46%.
While these numbers show that many organizations recognize the importance of third-party compliance, the gaps suggest that enforcement is inconsistent and that assumptions about vendor readiness may be putting PHI at risk.
These findings reinforce the idea that HIPAA compliance is a shared responsibility. Without strong vendor oversight and clear standards in place, even diligent internal teams remain exposed.
Common types of HIPAA violations and how to avoid them
When it comes to HIPAA violations, even small missteps can lead to costly consequences. Some violations happen due to poor security practices, while others stem from common administrative mistakes.
According to The HIPAA Journal, the most frequent violations fall into a few preventable categories. Here are some of the top violations to watch out for and real-world examples of how they were handled:
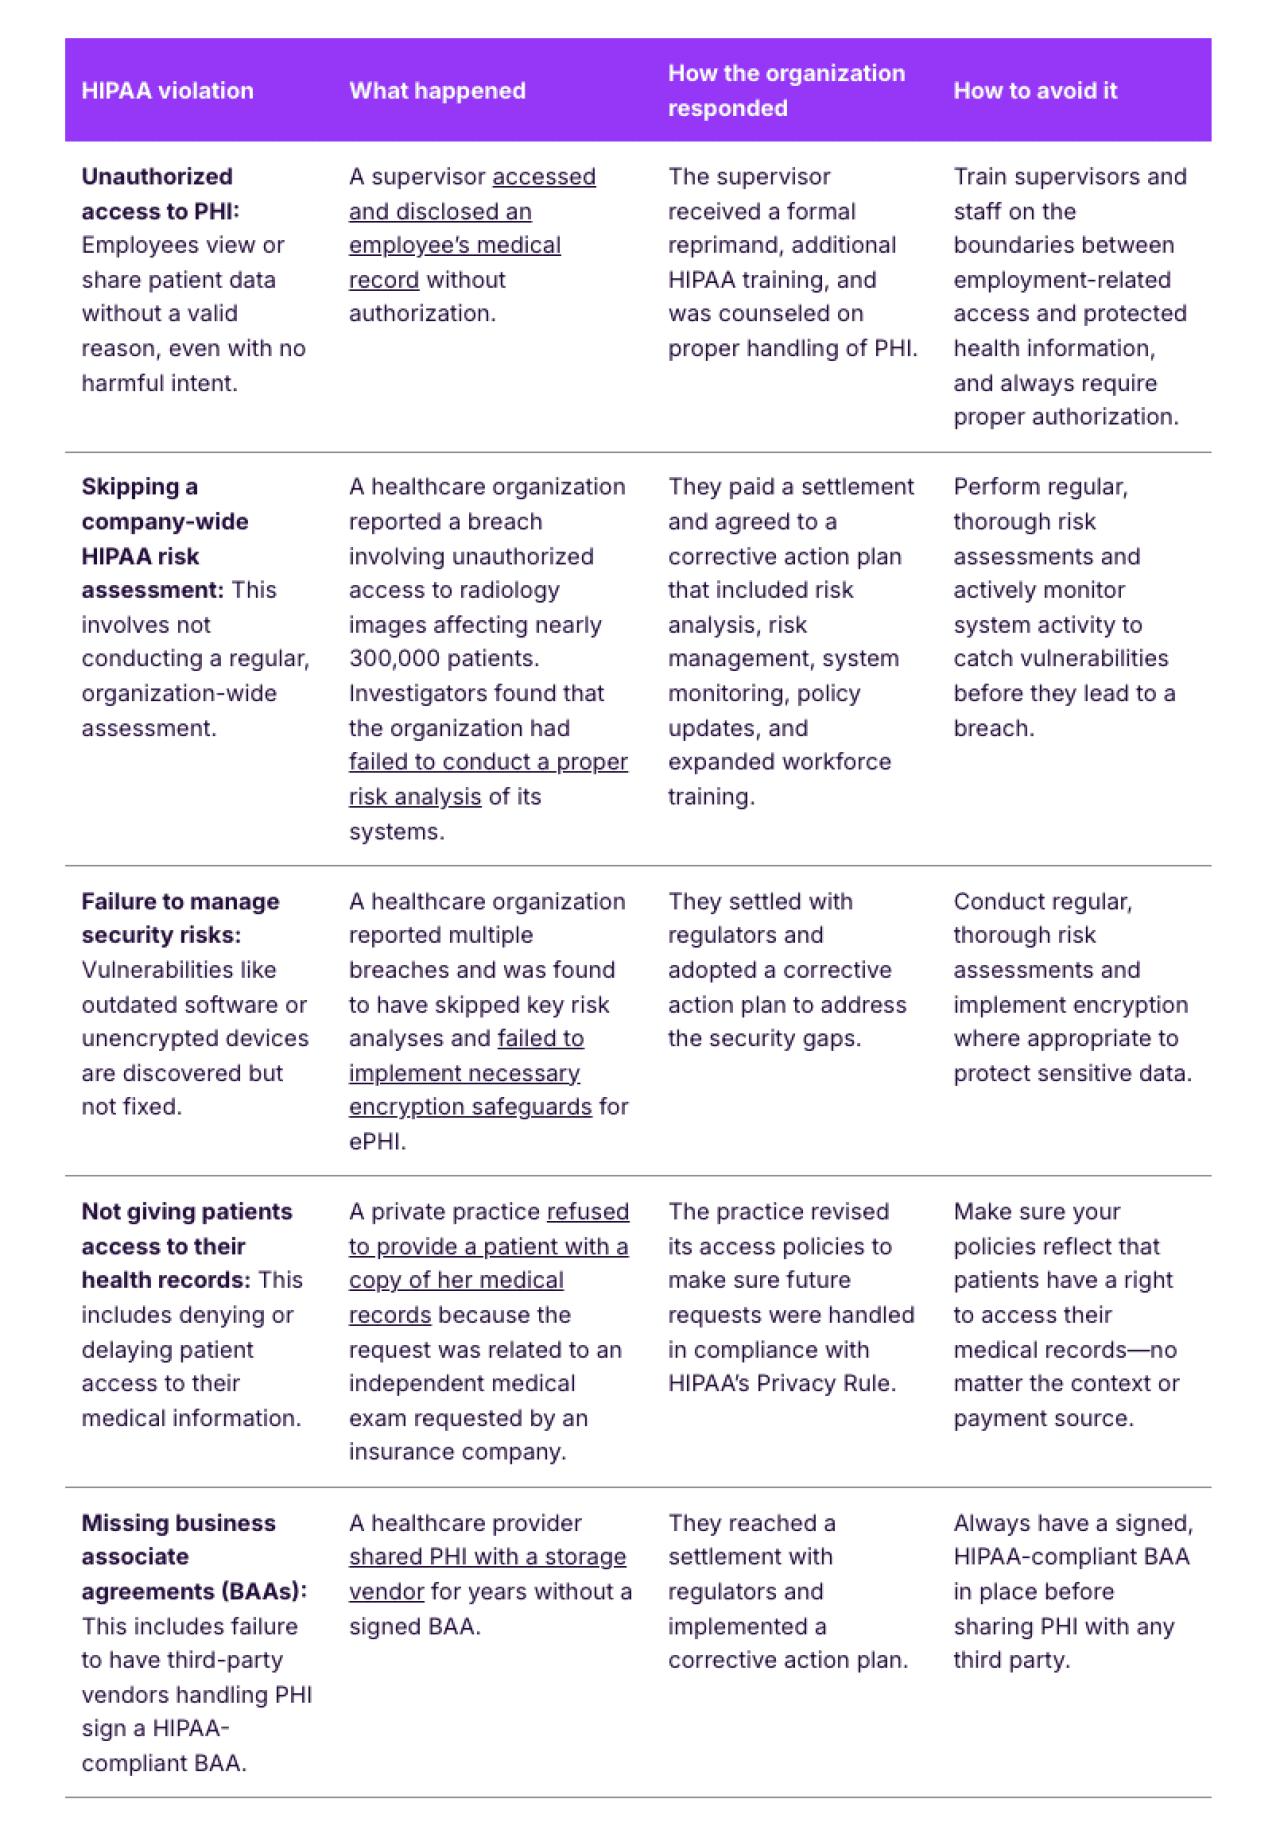
Investing in HIPAA compliance software can help reduce these risks by streamlining assessments and tracking vendor agreements. It’s a practical way to stay ahead of potential issues and build a more secure and compliant foundation.
Understand HIPAA violation penalties and the risks for your business
The importance of HIPAA compliance goes beyond avoiding regulatory action. Remaining compliant can protect your business from serious financial and reputational fallout.
To understand the risks, it’s helpful to know that HIPAA violations fall into two main categories: civil and criminal. Each carries its own consequences based on the nature of the violation and how your organization responds.
According to the U.S. Department of Health and Human Services (HHS), civil penalties are determined by its Office for Civil Rights (OCR), and criminal penalties are handled by the Department of Justice (DOJ).
Civil penalties are issued by the OCR and typically apply to organizations that fail to meet compliance requirements, either unknowingly or through negligence. They are broken down into four tiers:
- Tier 1 No knowledge: The organization didn’t know and couldn’t reasonably have known that a HIPAA violation occurred.
- Tier 2 Reasonable cause: The organization should have been aware of the violation, but couldn’t have avoided it. This is not considered willful neglect.
- Tier 3 Willful neglect—corrected: The organization intentionally ignored compliance rules but took steps to fix the issue within the allowed timeframe.
- Tier 4 Willful neglect—not corrected: This is the most serious civil offense. It occurs when a business knowingly violates HIPAA and doesn’t address the issue within the allowed timeframe.
Criminal HIPAA violations are enforced by the DOJ and usually involve individuals who misuse PHI for personal or malicious purposes.
According to HHS, civil fines can range from $127 to $63,973 per violation, with an annual cap of $1,919,173. Criminal penalties can reach up to $250,000 per violation and may also include one to 10 years in prison, depending on the intent and the harm caused.
Beyond the heavy fines, the reputational damage from a violation can be just as devastating for your business. Smaller businesses may not be able to recover from the financial losses and the loss of trust.
How HIPAA violations are typically discovered
HIPAA violations can come to light in several ways, and not all of them result from formal investigations.
In many cases, issues are first detected internally through routine monitoring or employee disclosure. Most electronic health record (EHR) systems have built-in monitoring tools that track who accesses patient records, helping businesses flag suspicious or unauthorized activity in real time.
Your organization should also conduct regular HIPAA compliance audits that review access logs, internal policies, and day-to-day practices. This makes it easier to identify gaps and prevent serious violations. Employees play a critical role by self-reporting accidental or suspected breaches, which can prevent minor issues from escalating.
You may also discover violations through external sources. Patients or anonymous individuals can submit complaints to healthcare providers, regulatory authorities, compliance officers, and government agencies. In more serious cases, the OCR may initiate a formal investigation following a complaint or breach notification.
Third-party audits and independent assessments can also surface vulnerabilities you may miss on your own. These reviews help strengthen internal controls and demonstrate a proactive approach to HIPAA compliance.
Closing the gap with smarter HIPAA compliance solutions
Avoiding a HIPAA violation means staying ahead of risks, not just reacting to them. Many organizations feel confident in their approach, but the reality is that blind spots still exist, especially around third-party partners, training, and keeping up with regulatory changes. Even well-meaning teams can miss something without the right systems in place.
That’s where a smarter solution makes the difference. Automated compliance tools can simplify your efforts and reduce the manual work needed to spot issues before they become problems. Automate HIPAA compliance and give your team the clarity and confidence to move forward securely.
Methodology
In May and June 2025, Vanta commissioned quantitative research by Centiment to explore knowledge gaps and confidence levels regarding HIPAA violations. The goal was to better understand how well U.S.-based professionals within the healthcare industry (business owners or manager-level and above) with some exposure to or influence over tasks related to PHI or HIPAA compliance can detect, respond to, and prevent HIPAA compliance issues. The survey collected responses from 613 healthcare professionals in the United States. Data is unweighted, and the margin of error is approximately +/-4% for the overall sample with a 95% confidence level.
HIPAA violations and breaches FAQ
Here’s a quick guide to some of the most common questions about HIPAA violations and breaches, including how they happen, what the penalties look like, and how to report them.
What is the penalty for a HIPAA violation?
Penalties vary based on how serious the violation is and whether it was accidental or intentional. Civil penalties can mean fines per violation, while criminal charges can lead to fines and prison time.
The more severe the violation and the less responsive your organization is to fixing it, the higher the stakes.
How quickly must a HIPAA breach be reported?
According to HHS, for breaches affecting 500 or more people, the covered entity must report it to HHS without unreasonable delay and in no case later than 60 days following discovery.
Breaches that affect fewer than 500 people are considered small breaches. These must be reported to HHS once a year by no later than 60 days after the calendar year ends.
The covered entity must also notify affected individuals and alert the media, if applicable, without unreasonable delay and no later than 60 days following discovery.
For companies that are business associates, breaches must be reported to the covered entity without unreasonable delay and no later than 60 days following discovery.
How do you report a HIPAA breach or violation?
Organizations must report breaches to the OCR using their online breach portal.
Patients, employees, and others can also file complaints within 180 days of the breach. Complaints need to include who was involved and what happened. Internally, companies should have clear policies and training in place so employees know how to flag issues and avoid escalation.
A note from Vanta: Vanta is not a law firm, and this article does not constitute or contain legal advice or create an attorney-client relationship. When determining your obligations and compliance with respect to relevant laws and regulations, you should consult a licensed attorney.
This story was produced by Vanta and reviewed and distributed by Stacker.
RELATED CONTENT: Understand Your Healthcare Privacy Rights
